Multiple CCIE holders including Cisco Emeritus. NSE8 (FCX) certified. Two-time APAC Fortinet Fabric Challenge champions. ISO/IEC 27001:2022 certified. ASD Cyber Security Partner. 100% Australian owned and operated.
01 / What we do
Four ways to work with Ip.Glass.
A project, an ongoing service, an assessment, or extra capacity. Each has a defined scope and a clear line between what we do and what stays with your team. Most clients start with one and grow into the others.
01 · Project
Design & deliver
A network or security project, designed and built to an agreed plan with a named technical lead.
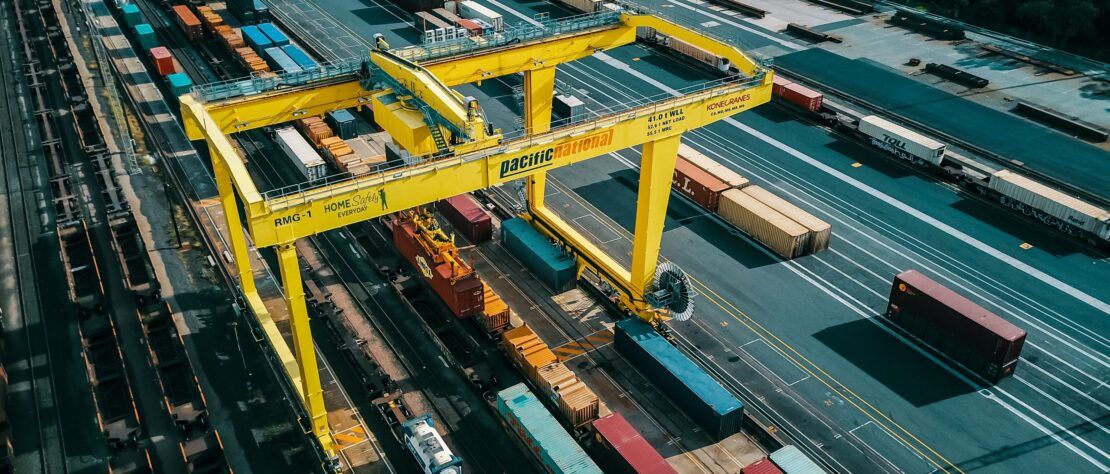
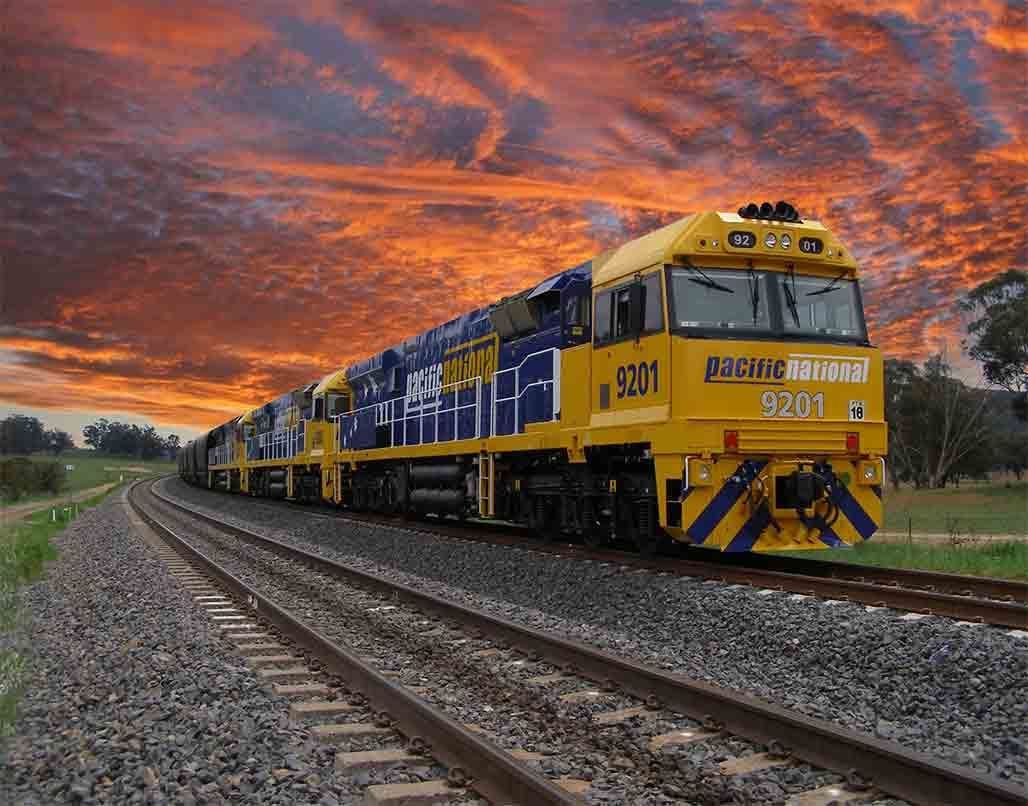
Enterprise network and security transformation across a national rail freight footprint, a single security fabric designed and delivered by Ip.Glass, then operated under a managed service.
Enterprise networking / Network security / Professional & managed services
Different operations. The same need for confidence.
We work where a network outage is an operational event, not an inconvenience. What that means differs by sector.
Critical infrastructure
Change with operational continuity in mind.
Obligations under the Security of Critical Infrastructure Act shape what must be evidenced, not just what must be secure. We align network and security decisions with the realities of essential operations: dependencies, access requirements and carefully planned change.
SOCI risk management program alignment and reporting artefacts
OT and IT segmentation that keeps vendor remote access working and logged
Change in approved windows, with rollback rehearsed, not assumed
Production runs on equipment that cannot be patched on a Tuesday night and protocols that predate authentication. We plan segmentation, remote access and network change around the systems and people that keep production moving.
Passive asset discovery: listen only, no active scanning on control networks
IEC 62443 zones and conduits mapped to how the plant actually runs
Secure remote access for OEMs and integrators with session recording
Dozens or hundreds of small sites, thin links, 24-hour operations and sites that rarely have technical staff on hand. Designed so a site needs no IT team of its own.
Zero-touch provisioning: a courier delivers it, the site plugs it in
SD-WAN with 4G/5G fallback and central policy for every site
NOC monitoring with ITSM integration and site-level service levels
Dealer networks, head office, importers and plants, bound together by manufacturer and finance integrations that must not drop. One security standard across sites you do not fully control.
A single policy baseline across dealer and corporate sites
Segmented, monitored integrations to manufacturer and finance systems
PCI DSS scope reduction for point-of-sale and finance environments
An administration centre, libraries, depots, pools and community halls, each built out at a different time, all expected to meet the same security standard on a public budget. We consolidate, then keep it simple to run.
Firewalling, secure access and visibility consolidated onto one platform
A programme across every facility, sequenced so services stay open
Essential Eight and audit evidence produced by the environment, not assembled by hand
Schools, early learning centres and community services spread across a region, supported by a small ICT team that is expected to keep services running and move the organisation forward. We give that team a platform it can manage.
Disparate point products replaced by one managed security fabric
Central management so a small team sees every site from one place
Safeguarding, filtering and identity controls that fit how campuses actually work
A managed-service partnership that is measured, automated where it should be, and owned by people who take it personally where it must be. You get the speed of a modern operation and the judgement of people whose names are on the work.
Data-driven
Decisions on evidence, not opinion.
Every environment we run is instrumented. Service levels, change outcomes and risk are measured, and the numbers drive what we fix next.
AI-assisted, engineer-owned
Faster, without losing the signature.
We use AI to accelerate the routine: analysis, documentation, first drafts of configuration and reporting. A named engineer owns and checks every output before it reaches you.
Visibility
You see what we see.
Within the agreed service scope, projects, tickets, changes and invoices are in one client view rather than a monthly report. No chasing for status.
A-team only
Ownership, by design.
Attitude over job title. The people on your account take the problem personally, see it through and tell you straight. A named technical lead stays with your environment from design into operation.
05 / The people behind it
Specialist by choice. Accountable by design.
A named technical lead, supported by the delivery and operations team, stays with your environment from design into operation. Security-cleared engineers are on the team for Australian Government work. Our reputation is built through the work we deliver.
Network and security services across Fortinet, Cisco, Palo Alto Networks, Zscaler, Juniper, HPE Aruba and Microsoft environments. Technology partners ↗
engineers and specialists
30+engineers and specialists
operations and support under managed-service agreements
24/7operations and support under managed-service agreements
offices: Sydney HQ, Melbourne, Hobart
3offices: Sydney HQ, Melbourne, Hobart
Australian owned and operated
100%Australian owned and operated
Let's start with your environment
A difficult project? A gap in capability? Let's work through it.
Tell us what needs to change. We'll discuss the context, identify where we can help and agree a sensible next step. We read every enquiry and reply within one business day.